A featured contribution from Leadership Perspectives: a curated forum reserved for leaders nominated by our subscribers and vetted by the Construction Tech Review Advisory Board.
Robinhood [Nasdaq: Hood]
7 Steps To Finding & Rapidly Deploying A New Compliance Capability
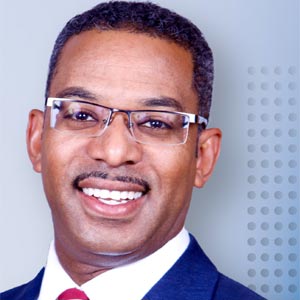
Lasalle Vaughn
People - Process - Technology: Keeping these three components in balance is at the heart of successful business operations. Unfortunately, some businesses integrate compliance capability into their ecosystem without a methodical approach and it can have devastating effects. I use a seven step approach — inclusive of people, process, and technology that helps to identify and deploy compliance capabilities.
People
1. Achieve alignment by considering stakeholder’s needs & regulatory requirements before looking for solutions.
Success or failure depends on buy-in from people—this is why people are often my first consideration when looking to achieve alignment. Start with the C-suite by sharing the needs, regulatory issues, risks, rewards, and timeline. As the firm gets closer to making a decision, keep the Financial Officer apprised of the range of costs involved. Without support from the top, adoption from the ranks tends to fizzle and fail.
Next, align all stakeholders who will use the compliance capabilities or be impacted by it. People tend to act for their reasons, not because compliance said so. To understand those reasons, consider hosting stakeholder meetings to gather their wants and needs—and enlist their help in designing solutions.
Include stakeholder needs along with any prioritized regulatory requirements in the formal Request for Proposal (RFP) so that the proposed compliance solution takes stakeholder requirements into account.
2. Build Support — designate change champions in every stakeholder group who evangelize the new compliance capability and support the change.
After the stakeholder intake sessions, request a volunteer from each stakeholder group to become the ‘change champion’ for that group. Most teams listen to their teammates first before going outside of their team. When an issue arises, this volunteer will have a vested interest to help triage issues and support the change for their group. This champion can be the eyes and ears for communications, training, and deployment.
Process
3. Refine the Workflow Tool — Ensure a simple, intuitive user interface is available.
Employees in the stakeholder groups may rely upon a workflow tool on a daily basis. A user interface can make or break adoption. Don’t settle for a clunky system that meets all regulatory requirements but is so difficult to understand that people intentionally avoid it. Insist on intuitive workflows. Engage stakeholder change champions once the choices have been narrowed down to the top three for demonstration meetings. If employees don’t think their colleagues will embrace the UI, they won’t.
It’s best to engage a user experience designer to assist here, and if that’s possible, make careful notes of the data needed and the number of clicks users have to use to get that data. On the flip side, a UI that doesn’t meet the firm’s regulatory requirements will cause problems down the road.
Move compliance technology companies up the selection list if they have an intuitive UI and agile engineers who can customize and design for both UI and regulatory requirements.
4. Cultivate Adoption — A change management framework must exist
Technology won’t work without people successfully adopting it. Adoption is best when it’s done well and only once—especially when deploying the compliance capability with firm wide impact.
Consult experts that utilize a change management framework with a language common to the firm. The common language guides both individuals and the organization by outlining clear goals with milestones, support, and a success blueprint. If the firm has a change management team, ask for help. If not, find a project manager to quarterback the roll-out from deployment to implementation.
5. Think Scalability — Can the compliance capability scale with the firm?
Far too often, firms make technology bets against their own success. Have a clear picture of how the firm’s needs will grow over time - in terms of data storage, transaction rates, user base, and location sets conditions for a firm to plan for scale. Build for the needs of the future, not just for needs today.
Also, make sure that the infrastructure can scale and that staff can support growth in utilization. It is not uncommon that high quality tools become more broadly used for things never intended.
Technology
6. Prioritize Security — Insist that the firm’s risk management standards are met
Protecting the firm and its customers’ information is one of the highest priorities. Work with the security team during the RFP process to vet each vendor. Know how each compliance capability meets regulations for privacy, including but not limited to GDPR, CCPA, FedRAMP, FINRA, the Code of Federal Regulations, etc.
Understand the regulatory certifications and frameworks (SOC1, SOC2, ISO, NIST) the compliance capability tool has, where their product lives (SaaS or on-prem), how data is transmitted, and how data is stored. Understand access controls, authentication, and confirm any history of data breaches (and how they handle them). Ensure that standard tools can be used such as SCIM user provisioning and SAML or OIDC single-sign on. Reject any technology that does not integrate with the firm’s SSO provider. The last thing users need is another password to manage.
Finally request copies of the compliance technology’s privacy, info/cyber security policies, application architecture, compliance assessments, and penetration tests. Request a review of these documents by the firm’s privacy and security teams. Have an onsite review and approval by the firm’s third party risk management team once the search has been narrowed to the compliance capability that best fits the firm’s needs.
7. Develop Reporting — Inculcate metrics and reporting in the initial roll out.
Quality reports share important metrics that deliver insights on how effective compliance controls and processes are operating. One important aspect of reporting is the ability to produce metrics in existing dashboards and tools. Adding yet-another-dashboard (YAD) makes it cumbersome to measure and understand the data.
Rolling Out Any Technology Is A Multi-Step Process With A Variety Of Pitfalls If People, Process And Technology Don’t Work Together” Lasalle Vaughn
Oftentimes, for many reasons, reporting functionality is delayed when firms purchase and deploy compliance capabilities. Work to avoid this temptation and push for reporting in the initial roll out. Actively enlist change champions to determine metrics that help their departments accomplish their goals. Compliance capabilities typically have key metrics in their off-the-shelf reports. Request a reports demonstration - during the evaluation period - with change champions present to ensure all important metrics can be tracked and included.
Rolling out any technology is a multi-step process. Avoid pitfalls by including People, Process and Technology upfront. Compliance capabilities are often an afterthought and may receive less attention than other technologies. However, successful roll out of any technology depends on keeping people, process and technology in balance, following a consistent framework and keeping the users in mind.
