

How to Increase Data Responsibility, Drive Business Transformation and Get Ready for the Eu's New Data Regulation
Jean-Claude Broido, Vice President, IBM Security Asia Pacific
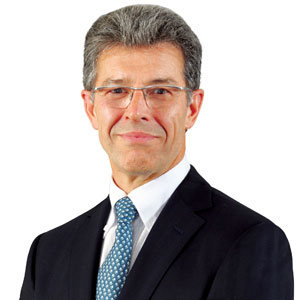
Jean-Claude Broido, Vice President, IBM Security Asia Pacific
Data is the phenomenon of our time, driving important advances and more effective decision making in business, government and society. At IBM we have a long-standing view that organizations that collect, store, manage or process data have an obligation not only to protect it, but to handle it responsibly.
As the data economy continues to rapidly evolve, Governments around the world are responding with new legal frameworks. The European Union’s General Data Protection Regulation (GDPR) was established in 2016 to harmonize data privacy laws across Europe, protect the data privacy of individuals across the EU (“data subjects”) and reshape the way in which organizations use and protect data. Enforcement starts on May 25th 2018, after which time, non-complying organizations could potentially face heavy fines. With just over 50 days to go before the deadline, time is running out.
The GDPR provides a single set of data protection and privacy rules across the European Union’s (EU) 28 member states. Personal data—regardless of where in the world it is stored, processed or distributed—must be protected, and proof of protection must be verified. The GDPR also requires organizations to report certain classes of data breaches within 72 hours and to quickly respond to requests from EU data subjects to access, correct or delete their personal data.
Any organization that offers goods or services in the EU, or collects information about EU data subjects are impacted–including those companies from the Asia Pacific region which should act now to understand what they need to do to comply.
• Data: look at the entire life cycle management of personal data. This includes: steps to discover and assess what personal data you have within your organization; ensuring the quality and integrity of that data; defining how you are using the data; and, how you can better interact with individual customers, clients or third parties in relation to their data. The process should involve not only the appropriate use of personal data, but also consent, choice, access, rectification and erasure of such data.
• Privacy: assess your current data privacy practices and determine what changes are required to prepare for the GDPR. Classify systems, identify potential risks and implement a privacy-by-design approach to IT systems management. The process should involve not only the protection of fundamental privacy rights, but also the security and confidentially of personal data.
• Protection: put in place strong technical and organizational measures (TOM’s) around cybersecurity, encryption, access controls and monitoring, incident breach monitoring and management. If you use cloud computing services, use those that support global data privacy standards and country-specific privacy laws about cross-border data transfer and processing.
• Governance: determine how to quickly and securely classify, manage and deliver data to only users who have a genuine and justifiable need. Ensure end-to-end traceability of personal data across the organization and lifecycle of the data and ensure effective risk assessment and management of third-parties involved in handling personal data.
• People, Processes and Communications: train employees about GDPR requirements, because they will need to understand not only the risks, but also the potential impact—financial and reputational— from improper use of data. Look at current business processes, which include HR, CRM and others that are heavily dependent upon personal data, and determine how you can successfully manage the changes required by the GDPR.
While GDPR can be considered another regulatory burden for organizations, compliance can help to accelerate digital transformation by introducing more efficient and integrated data analysis.
Overall, developing trust-driven relationships, investing in sustainable and governed data assets, ensuring data privacy and security, are fundamental to creating a company-wide culture of data responsibility— which we believe is the cornerstone of every good business

